TL;DR

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
A developer has posted a reconstructed source code of the notorious cyber-weapon Stuxnet on Show HN, aiming for educational use. The release has attracted significant attention, raising questions about security and historical understanding.
A developer has publicly posted a reconstructed version of Stuxnet’s source code on the platform Show HN, claiming it is intended solely for educational research. This move has reignited widespread interest in the infamous cyber-weapon, which historically targeted Iran’s nuclear program. The release is notable because the original source code of Stuxnet has been classified and unavailable for public study, making this reconstruction significant for cybersecurity historians and researchers.
The source code was shared by a developer known only as ‘researcher’ on Show HN, a platform for sharing projects and ideas. The code is described as a reconstruction, not an original leak, and the poster emphasizes it is for educational purposes only. While the authenticity of the code has not been independently verified, initial analysis suggests it closely resembles known components of Stuxnet, a highly sophisticated malware believed to be developed by nation-states to sabotage Iran’s nuclear facilities. The timing of the release coincides with a spike in public and media interest in cyber-espionage and cyberwarfare, driven by recent geopolitical tensions and a surge in cybersecurity research activities.Cybersecurity experts and analysts have responded with caution, noting that the code’s authenticity remains unconfirmed by independent sources. Some researchers have expressed concern that such disclosures could aid malicious actors, while others see it as a valuable resource for understanding cyber-attack techniques and the evolution of malware. The original Stuxnet, discovered in 2010, was a zero-day exploit targeting Siemens industrial control systems, and its source code has long been considered a state secret.
Potential Impact on Cybersecurity and Historical Understanding
Revealing a reconstructed version of Stuxnet’s source code could significantly influence cybersecurity research by providing deeper insights into one of the most sophisticated malware ever created. It offers scholars and security professionals a rare opportunity to analyze the malware’s structure, techniques, and operational logic, which could inform future defensive strategies. Additionally, the release raises questions about the accessibility of classified cyber tools and the implications for international security, as knowledge of such malware can be exploited by malicious actors. However, the true impact depends on the authenticity of the code and how it is used or interpreted by the community.Products Worth Considering

EcoFlow Smart Home Panel 2 Whole-Home Backup System Hub
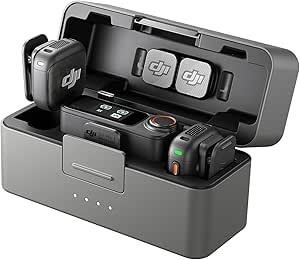
DJI Mic 3 Wireless Microphone System (2 Transmitters, 1 Receiver, Charging Case)

Samsung Galaxy Tab S10 FE 128GB Wi-Fi Android Tablet, Blue
As an affiliate, we earn on qualifying purchases.
Historical and Technical Background of Stuxnet
Stuxnet was first identified in 2010 as a highly advanced computer worm targeting Iran’s nuclear centrifuge facilities. It is widely believed to have been developed by the United States and Israel as part of a covert operation to delay Iran’s nuclear program. The malware was notable for its complexity, use of multiple zero-day vulnerabilities, and ability to manipulate industrial control systems while hiding its presence. Despite its notoriety, the actual source code of Stuxnet has never been publicly available, with details only pieced together through cybersecurity investigations and reverse engineering efforts. This scarcity of information has contributed to its mythic status in cybersecurity history. The recent posting of a reconstructed code marks a rare event that could reshape understanding of this cyber-weapon’s inner workings.Authenticity and Security Implications of the Reconstructed Code
It is not yet confirmed whether the posted source code is an exact reconstruction of the original Stuxnet malware or a close approximation. Independent verification by cybersecurity experts is pending. There are concerns that the code could be incomplete or altered, and its public availability raises questions about potential misuse or misinterpretation by malicious actors. The true origin and authenticity of the posted code remain unverified at this stage.Verification, Community Analysis, and Policy Responses Pending
Cybersecurity researchers and analysts will likely undertake detailed verification and analysis of the posted code to assess its authenticity and technical details. Discussions within the cybersecurity community will determine whether the code can be reliably used for research and education. Meanwhile, policymakers and security agencies may evaluate the implications of this disclosure, considering whether it affects ongoing cyber defense strategies or international cybersecurity norms. The developer has indicated that further updates or clarifications may follow as analysis progresses.Key Questions
Is the posted source code the original Stuxnet code?
It is currently unconfirmed whether the posted code is an exact copy of the original Stuxnet source code. Experts are awaiting verification.
What are the risks of sharing reconstructed malware source code publicly?
Sharing such code could potentially aid malicious actors, but it also offers educational value for cybersecurity research. The impact depends on authenticity and usage.
Why was the source code not publicly available before?
The original Stuxnet source code was classified and believed to be a state secret, due to its sensitive nature and potential security implications.
Could this lead to new cybersecurity threats?
If the code is authentic and misused, it could inform new attack techniques. However, verification and analysis are needed to assess this risk.
How might this influence future cybersecurity research?
Access to the code could deepen understanding of advanced malware, improving defensive strategies and threat detection capabilities.
Source: hn