TL;DR

Get privacy and security gear delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
Deepfakes are images, audio, or video generated or altered with AI to make a person appear to say or do something they never did, and they’re one slice of the broader category of synthetic media. No single trust signal — watermark, label, metadata, or AI detector — proves a file real or fake, because each can be stripped, spoofed, or simply absent. The reliable habit is to verify the source, date, and context of media and corroborate with independent reporting before you believe or share it.
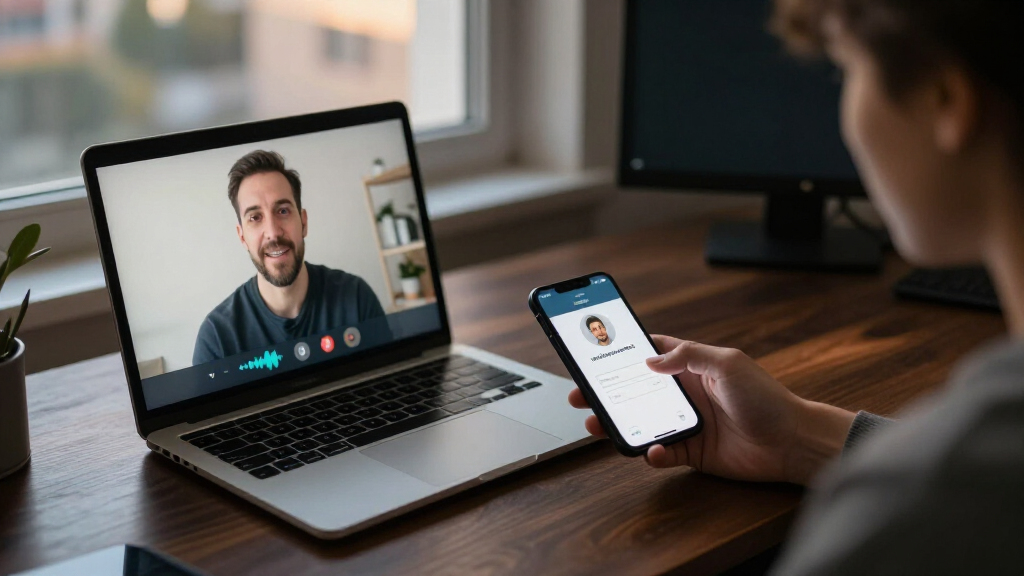
Imagine getting a voicemail from your boss’s actual voice — the cadence, the little laugh, everything — asking you to wire money by end of day. The voice was cloned from a three-minute conference call. Scenarios like this are no longer hypothetical; voice cloning now requires only seconds of reference audio and tools cheap enough that anyone can use them.
That’s the uncomfortable reality behind deepfakes and the wider world of synthetic media. The good news: you don’t need a forensics lab to protect yourself. You need a small set of habits and a clear understanding of what trust signals — provenance records, content credentials, platform labels — can and cannot tell you.
In this guide, you’ll learn what deepfakes actually are, why “looking for glitches” no longer works, how trust signals function and where they fail, and a step-by-step verification routine you can run on any suspicious clip in under five minutes.
Deepfakes are media generated or altered with AI to make a person appear to say or do something they never did; synthetic media is the broader category and inc…
Visual glitch-hunting no longer works — high-quality fakes have few tells, and real footage can look strange from compression, so verify source, date, and cont…
No single trust signal is a guarantee: metadata gets stripped, watermarks get removed, labels can be wrong, and missing credentials prove nothing about authent…
Run the 5-step routine on suspicious clips: pause, trace the original source, check date and completeness, search for independent coverage, and verify through…
For voice-clone scams targeting you or family, the defense is procedural, not perceptual — hang up and call back on a number you already have.
MEDIA LITERACY / FIELD GUIDE 01
Deepfakes, Synthetic Media and Trust Signals Explained
A convincing face or familiar voice is not proof. Deepfakes are one part of synthetic media, and no watermark, label, metadata record, or detector can settle authenticity alone. Verify the source, date, and context before you believe or share a striking clip.
What counts as synthetic media?
The key distinction is whether generated media borrows a real person’s identity or likeness.
Deepfake
AI-generated or altered image, audio, or video that makes a person appear to say or do something they never did. The defining feature is impersonation.
Synthetic media
Includes deepfakes, fully generated images, cloned voices, AI music, and virtual characters—even when no real person is being imitated.
Use and disclosure
A fictional city made for a film is synthetic. A cloned mayor announcing a false evacuation impersonates identity and authority. Consent and context matter.
Why glitch-hunting fails
Visual inspection can miss convincing fakes and wrongly cast suspicion on genuine footage.
Trust the context more than the pixels.
Modern tools can make convincing media quickly and cheaply. Compression, low light, and bad uploads can also make real footage look strange. Neither polish nor glitches deliver a verdict.
An old recording can be presented as breaking news. Check the publication date and original event.
A crop can remove the question or surrounding speech. Find the complete recording before interpreting a quote.
Selective editing can distort meaning without changing a single pixel or using AI.
Automated tools can help prioritize review, but accuracy varies and false positives and negatives occur.
Four useful checks—and their limits
Treat each signal as one piece of evidence. Combine clues and corroborate the claim itself.
| Signal | What it can tell you | Where it can fail |
|---|---|---|
| Provenance records | ✓Where a file came from and recorded edits along its chain of custody. | ~Only useful when preserved end to end; a valid record does not prove the accompanying claim is true. |
| Credentials & watermarks | ✓Embedded metadata or labels may indicate AI involvement or editing history. | ✗Metadata can be stripped; watermarks can be removed or never added. |
| Platform labels | ✓A notice may disclose that content was generated or manipulated. | ~Labels can be missing, wrong, or inconsistent between platforms. |
| Independent verification | ✓Reputable reporting, original publishers, or people directly involved can corroborate a claim. | ~It takes time; early reports can also be wrong. |
Read the absence carefully: missing credentials or an AI label do not prove a file is authentic—or fake. Signals can disappear during ordinary copying, cropping, editing, and re-uploading.
Run the five-step verification routine
When a striking clip lands in your feed, take a moment to check its trail. For urgent claims, verify through a known contact channel before acting.
Stop the impulse
Do not forward, repost, or act while the claim is still unverified.
Find the original
Look for the earliest source, publisher, or full recording—not just a repost.
Date and completeness
Confirm when it was made and whether the surrounding footage changes the meaning.
Search independently
Check reputable reporting and other sources unrelated to the original post.
Use a known channel
For urgent requests, call the person or organization using a number you already have.
A trustworthy habit is a chain, not a single badge.
Protect people and consent
Nonconsensual sexual imagery, impersonation scams, harassment, and political misinformation can cause serious harm. Private individuals can be targets too.
Watch for the “liar’s dividend”
Convincing fakes can make people dismiss genuine evidence as fabricated. Evaluate each recording on its source and corroboration.
What Deepfakes and Synthetic Media Actually Are (In Plain English)
Deepfakes are images, audio, or video generated or altered with AI to make a person appear to say or do something they never did. The word itself comes from “deep learning” plus “fake,” and the defining feature is impersonation: the content borrows a real person’s face, voice, or likeness [1].
Synthetic media is the bigger umbrella. It covers deepfakes plus fully generated images, cloned voices, AI music, and virtual characters that may not imitate anyone at all. An AI-generated illustration of a city that doesn’t exist is synthetic media, but it isn’t a deepfake — nobody is being impersonated [1].
This distinction matters because the ethical question changes with the use. Imagine a filmmaker creating a fictional city for a science-fiction movie: the image is synthetic, but viewers understand it as art. Now imagine someone using a cloned mayor’s voice to announce a fake evacuation order. Both involve generated media; only the second falsely borrows a real person’s identity and authority. The technology alone doesn’t determine the harm. Consent, disclosure, and whether people are being misled do.
Synthetic media can also be useful when its role is clear. A documentary might synthesize a narrator’s voice with consent, or a game studio might build a virtual character from scratch. The tradeoff is that disclosure needs to travel with the content: if an excerpt is separated from the film or game and shared without its original context, viewers may mistake what they see for evidence about a real person or event [1].
Think of it like Photoshop, but with a much lower cost and a wider range of media. Photo manipulation has existed for a century; what’s changed is speed and accessibility. According to vultrade.com, production costs and technical barriers have fallen sharply as generative tools have become more accessible [1]. A fake doesn’t need to be flawless to cause harm: a convincing-enough voice message delivered during a rushed workday may prompt action before anyone thinks to verify it.
Why You Can’t Spot Deepfakes by Looking for Glitches Anymore
No, you cannot reliably spot deepfakes by eye or ear anymore. Early deepfakes had tells — blurry edges around the face, hands with six fingers, a voice that flattened every vowel — but current tools produce material with few obvious flaws, and they do it quickly and cheaply [1].
Worse, the old tells now mislead in both directions. A genuine video can look strange because of aggressive compression, low light, or a bad upload — the pixel smears you were told to hunt for. Meanwhile a polished, familiar-looking clip proves nothing about whether the event actually happened [1].
Here’s the trap most people miss: context matters as much as the media itself. A completely real clip can mislead through selective editing, a false caption, or an old recording presented as breaking news. Cropping a politician’s answer to remove the question can distort meaning without touching a single pixel [1].
For example, a short video may show a politician saying, “We will close the shelters.” Shared alone, it sounds like an announcement. The full recording might show the speaker was quoting a proposal they oppose. The words and the face in the clip are genuine, but the edit changes who appears to hold that position. Checking the full speech and its date can reveal that gap; staring more closely at the speaker’s face cannot.
A concrete example: a video circulated showing an official appearing to stumble through a speech. The footage was real — but it was three years old and had been re-cropped to remove the fact that the official was reading a tribute to a colleague who had just died. No AI manipulation. Total deception. That’s why verification has to go beyond artifact-hunting: check the source, the date, the surrounding footage, and independent reporting — not just the visual surface [1].
Trust the context more than the pixels. A perfect-looking video from an anonymous account deserves more suspicion than a grainy one from a named, accountable source.
Trust Signals Explained: The Four Checks That Actually Help
Trust signals are pieces of evidence about a file’s origin and history that help you judge authenticity — but none of them is a complete guarantee. According to vultrade.com, the four most useful signals are provenance records, content credentials, platform labels, and independent verification [1].
| Trust Signal | What It Tells You | Where It Fails |
|---|---|---|
| Provenance records | Where a file came from and how it was edited — a chain of custody | Only helps if preserved end to end; many workflows strip it |
| Content credentials / watermarks | Embedded metadata or labels indicating AI involvement or edit history | Metadata is stripped when files are copied or edited; watermarks can be removed or never added |
| Platform labels | A notice that content was generated or manipulated | Labels can be wrong, missing, or inconsistent across platforms |
| Independent verification | Confirmation from reputable outlets, original publishers, or people directly involved | Slowest signal; early reports can be wrong too |
Think of provenance as a travel log attached to a file: it can show where the file started and what edits were recorded along the way. That history is useful when intact, but it describes the file’s path, not whether every claim made about it is true. A credentialed image of a real street could still be posted with a false caption claiming it shows a protest today.
Watermarks and labels help people recognize AI involvement, but they depend on systems and people preserving them. A creator might export a labeled image, then a viewer might screenshot and crop it; the new copy may lose the metadata or visible mark. That creates a practical tradeoff: signals can make transparent sharing easier, yet relying on them alone leaves gaps whenever content moves between tools and platforms.
Platform labels have a similar limitation. A notice can tell you that a platform identified or was told about AI use, but it may not explain whether the change was minor, like noise removal, or substantive, like replacing someone’s words. Read the label as a prompt to ask what was changed, not as a full account of the media’s meaning.
Independent verification adds another kind of evidence: someone else has checked the source or event. For instance, if a clip claims that a city has closed its bridges, a statement from the city and separate reporting from local outlets can help confirm what happened. This check may take longer, and early reports can be mistaken, but agreement among sources with different access is harder to fake than a single post.
Here’s the critical nuance: these signals cut both ways. A valid provenance record doesn’t prove that a claim attached to the media is true — you can have a properly credentialed AI image shared with a false caption. And missing credentials don’t prove something is fake: many authentic files have no watermark or metadata at all [1].
Adoption is also uneven. Some camera systems and creative tools now attach credentials at creation, but many platforms and sharing pipelines don’t preserve them through to what you see in your feed. Treat every signal as a clue needing corroboration, never a verdict [1].
The 5-Step Verification Routine to Run Before You Share Anything
When a striking clip lands in your feed, run this routine before sharing or acting on it. It takes about five minutes and catches most deceptive media — synthetic or not [1].
- Pause. Emotional urgency is the manipulator’s favorite tool. If a clip makes you furious within seconds, that’s exactly when to slow down.
- Trace the original source. Find the earliest posting you can. Who uploaded it first, when, and what do you know about that account? Anonymous fresh accounts deserve extra suspicion.
- Check the date and completeness. Is this current, or an old recording recycled? Is the clip full-length or cut to remove context?
- Search for independent coverage. If a public figure genuinely said something explosive, multiple outlets will report it within hours. Silence is a signal.
- Verify through a known channel. For urgent claims — a payment request, a family emergency, a “CEO” voice message — contact the purported person or organization using a number you already have, not one supplied in the message.
That last step matters most in voice-clone impersonation scams, which increasingly target private individuals rather than public figures. A grandparent gets a tearful call that “sounds exactly” like a grandchild in trouble. The defense isn’t detecting the fake — it’s hanging up and calling the grandchild’s real number [1].
Notice what this routine doesn’t include: running the file through an AI detector. Detector scores can help investigators prioritize, but their accuracy varies wildly across tools and media types, and they produce both false positives and false negatives. A detector result is one piece of evidence, not a verdict [1].
Who Gets Hurt: Why Deepfake Harms Don’t Spread Evenly
The harms from deceptive synthetic media fall hardest on people who never asked to be public figures. According to vultrade.com, the main damage categories are nonconsensual sexual imagery, impersonation scams, harassment, and political misinformation [1].
Public figures — politicians, celebrities, journalists — get the headlines, and they are frequent targets. But private individuals face the sharpest harms. Nonconsensual intimate imagery overwhelmingly targets women, and victims often find the material resurfacing for years after the first takedown. Impersonation scams hit ordinary people’s bank accounts directly [1].
Consent, privacy, disclosure, and the ability to challenge misuse are the central issues here. If someone uses your likeness or voice, you should have the right to know, refuse, and get it removed. That principle is simple; the enforcement is not — laws vary by jurisdiction and keep changing, covering fraud, impersonation, harassment, and election-related deception differently depending on where you live [1].
There’s also a subtler harm: the “liar’s dividend.” When everyone knows convincing fakes exist, dishonest people can dismiss authentic recordings as fabricated. The real clip of a real scandal gets waved away as “probably AI.” Deception and doubt are two sides of the same coin — synthetic media doesn’t just create false beliefs, it erodes the value of true evidence [1].
If your likeness or voice is misused: save copies and links, document where and when the material appeared, report it to the platform, and seek legal or victim-support advice. For financial impersonation, contact your bank immediately through a verified number [1].
If You Create or Publish: Four Habits That Keep You Credible
Creators and publishers hold one side of the trust problem, and the bar is rising. If you produce or distribute media, four habits from vultrade.com’s guidance protect both your audience and your reputation [1].
- Disclose meaningful AI alterations. If you synthesized a voice, extended footage, or generated imagery, say so. Undisclosed manipulation that later surfaces destroys far more trust than honest labeling ever costs.
- Get permission before using someone’s likeness or voice. Consent isn’t a legal technicality in most jurisdictions — it’s the difference between a creative tool and an impersonation.
- Preserve provenance where possible. Keep edit histories and content credentials intact through your workflow instead of stripping metadata by default.
- Correct misleading material promptly. Speed of correction, not perfection, is what sustains credibility.
A small newsroom example makes this concrete. A regional outlet used an AI-upscaled version of a blurry eyewitness photo — a legitimate enhancement — but labeled it inline as “image enhanced for clarity.” When a reader questioned the photo’s authenticity weeks later, the disclosure ended the controversy in one reply. The same photo, unlabeled, would have become a credibility crisis.
For journalists verifying a suspicious recording specifically: trace it to the earliest available source, review the full recording and metadata, compare against independent evidence, and consult relevant experts. And communicate uncertainty honestly — presenting a detector score as proof is itself a form of misinformation [1].
Frequently Asked Questions
What’s the difference between a deepfake and synthetic media?
A deepfake is AI-generated or manipulated media that imitates a real person — their face, voice, or likeness. Synthetic media is the broader category and includes content that may not imitate anyone, like fully generated images, AI music, or virtual characters. Every deepfake is synthetic media, but not all synthetic media is a deepfake [1].
Can AI detection tools reliably tell if a clip is fake?
They can provide useful signals, but results are uncertain and vary by tool, media type, and conditions. Detectors produce both false positives and false negatives, especially as generation methods change. A detector score should be one piece of evidence — never the sole basis for a high-stakes judgment [1].
Does the absence of a watermark or AI label mean content is authentic?
No. Many authentic files carry no watermark or metadata at all, and generated content may lack a watermark or lose one during editing and sharing. Metadata is routinely stripped when files are copied or re-uploaded. Missing credentials prove nothing in either direction [1].
Can a completely real video still be misleading?
Yes. Cropping, splicing, misleading captions, or false dates can distort genuine footage without altering the underlying pixels. A real clip presented with the wrong context — like old footage recycled as breaking news — can deceive as effectively as a deepfake [1].
What should I do if someone misuses my likeness or voice?
Save copies and relevant links, document when and where the material appeared, report it to the platform, and seek qualified legal or victim-support advice. If the misuse involves financial impersonation, contact the affected bank or organization immediately using a verified phone number [1].
Are deepfakes illegal?
It depends on the use and the jurisdiction. Laws may address fraud, impersonation, harassment, nonconsensual sexual imagery, election-related deception, or privacy — but rules vary widely and continue to evolve. Consent-based creative uses may be perfectly legal in one context while nonconsensual uses of the same technology are criminal in another [1].
Conclusion
Here’s the one habit to carry forward: never let a single piece of media — however vivid — be your only source of truth. Verify the source, the date, and the claim against something independent before you share, believe, or act. That discipline protects you against deepfakes, cheap edits, recycled clips, and plain false captions all at once.
The next time a video makes your jaw drop and your thumb hover over “share,” ask one question first: who posted this, and who else can confirm it? Five seconds of curiosity beats five minutes of regret.
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.