TL;DR

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Infrastructure as Code defines cloud resources in files, but applying those files can expose data, widen access, interrupt service, or delete resources. Review each change like application code: understand the intent, inspect the generated plan and environment, use automated checks as support, and scale scrutiny to the change’s impact.
A one-line infrastructure change can open a door across an entire cloud account. Imagine a pull request that appears to adjust a storage setting; the generated plan shows that it will replace a production resource instead. The code fits on a screen. The consequences may reach customers.
Infrastructure as Code (IaC) defines cloud resources, networks, access controls, and deployment environments in files that teams can version and automate. Because those files can create, change, or delete real infrastructure, they deserve the same careful review as application code. You’ll learn what to inspect, why a clean diff is not enough, and how to make reviews practical without slowing every routine update.
IaC can create, modify, or delete live cloud resources, so review its effects before deployment.
Read the generated plan for replacements, deletions, permission changes, and the target environment.
Use scanners and policy checks to find known patterns, then judge their meaning in context.
Check shared module callers, versions, state access, secrets, and drift as part of the change.
Match review depth to production impact, data sensitivity, access, and recovery needs.
Infrastructure • Review • Operations
Why Infrastructure as Code Needs Review Like Application Code
Infrastructure files can change real systems. A short diff may expose data, widen access, interrupt service, or delete a resource. Review the intent, generated plan, and target environment before deployment.
Key insight
A clean diff does not prove a safe deployment.
01 / Why review matters
IaC is operational logic
Applying configuration can create, change, or remove live cloud resources. The review question is not only whether the files parse; it is whether the change does what the team intends, in the right environment, with a risk the team understands.
Security
Who can reach it?
Network rules and identity permissions can open paths to services or grant access to more data than a workload needs.
Availability
Will it stay online?
A setting that triggers replacement can interrupt a production service or require a maintenance window and migration plan.
Data
What could be exposed or lost?
Storage, database, backup, and encryption changes affect sensitive information and the ability to recover it.
02 / A practical review path
Follow the change from intent to impact
A useful pull request gives reviewers enough context to connect the code to the systems, users, and data it affects.
Read the purpose
Check the change against a specific, stated goal.
Inspect the plan
Find creates, updates, replacements, and deletions.
Verify the target
Confirm account, environment, state, and callers.
Judge the risk
Check access, data, recovery, and deployment safeguards.
03 / Code versus plan
Read what the tool expects to do
Modules, variables, provider behavior, and existing state shape the result. A generated plan adds operational context that a source diff alone may not show.
Scan the plan for
Pause on destructive actions and confirm whether downtime, migration, or recovery steps are needed.
Then verify the context
04 / Automation + judgment
Checks catch patterns; people assess meaning
Formatting and validation can catch structural problems. Scanners and policy rules flag known risky patterns. Neither can establish that a change is safe for a particular service and environment.
Find repeatable issues
- ✓Formatting, syntax, and unsupported fields
- ✓Known policy violations and risky settings
- ~May miss combinations or create noisy alerts
Connect change to purpose
- ✓Check permissions against the workload’s needs
- ✓Assess production impact, data sensitivity, and recovery
- ~Needs clear ownership and a focused change
05 / Proportional scrutiny
Match review depth to potential impact
Use the change’s reach and consequences to focus attention. Identity, network, production, and sensitive data changes warrant a closer look than routine low-risk development updates.
Protect the whole path to deployment
Pair review approvals with least-privilege deployment credentials, protected environments, secure state access, and audit logs. Keep plans and secrets from leaking into comments or logs.
Treat infrastructure changes like changes to a live system
Infrastructure as Code needs review like application code because its instructions can change running systems, not just produce a different screen or calculation. An applied change can create a resource, alter who can reach it, interrupt a service, or remove something people rely on. Review gives the team a chance to understand those effects before they happen.
Think of IaC as a set of building instructions that can move the doors and walls of a working building. A small edit to a network rule might let a service communicate with a new system, or make a path reachable from the public internet. A permission change might let a task read more data than it needs. The file can look tidy while its effect is wide.
For example, a developer updates a setting on a cloud storage bucket to make a test integration work. The change appears harmless in a short diff, but the setting also affects how the production bucket handles access. A reviewer who asks which environment the change reaches, and what data the bucket holds, may catch the mismatch before deployment.
That is why review asks more than “Will this parse?” It asks whether the change matches the stated goal, whether its effects fit the system, and whether the team understands the risk if the plan goes wrong. As with an application bug, the safest moment to catch an unintended behavior is before it reaches the people who depend on the service.
Products Worth Considering

Samsung 27 Odyssey OLED G5 (G50SF) QHD QD-OLED Gaming Monitor

Samsung 27-Inch Odyssey QD-OLED G8 4K 240Hz Gaming Monitor

LG UltraGear 27-Inch QHD OLED Gaming Monitor, 240Hz, 0.03ms, G-SYNC Compatible, FreeSync Premium Pro, HDMI 2.1
As an affiliate, we earn on qualifying purchases.
Read the generated plan to see what the code will really do
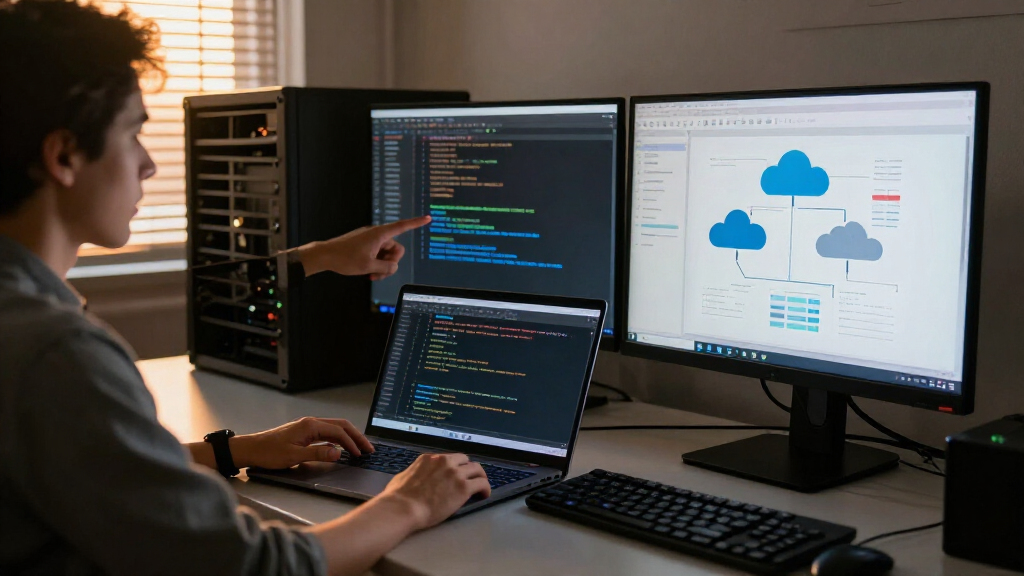
Review the generated plan as well as the IaC files, because the plan shows how the tool expects to change resources in a particular environment. Source code describes intent; a plan helps reveal operational impact, such as resources it will create, update, replace, or delete. That difference matters when modules, variables, provider behavior, and existing state all shape the result.
A small diff can hide a large consequence. Imagine a team changes the machine type for a production service and expects an in-place update. The plan instead shows a replacement, which could affect availability or discard data if the resource is not designed for replacement. The reviewer can pause, check the resource’s role, and ask whether a maintenance window or migration is needed.
Start with the plan’s most consequential actions. Look for deletions and replacements, then check updates to identity, network paths, and data storage. Confirm which account and environment the plan targets, and compare that with the pull request’s stated purpose. A plan without clear environment context is like a map without a street name: hard to trust, even if the lines look neat.
Plans also need careful handling. They may expose sensitive values, depending on the tool and configuration. Keep access limited, avoid copying secret values into comments or logs, and follow the tool’s guidance for protected data. A readable plan helps a reviewer; an indiscriminately shared plan can create a different security problem.
Check access, networks, and data before you approve
Check permissions, network exposure, and data handling first because these changes can alter who reaches a service or what information it can use. A formatting check can confirm that a file follows a style; it cannot tell you whether a role needs access to every object in a bucket. Human review connects the configuration to the system’s purpose.
Picture a service that processes invoices. Its new role needs permission to read a queue and write results to one storage location. If the change grants broad access across the account, the configuration may still validate, but it gives the service more reach than the task calls for. A reviewer familiar with the service can ask for narrower permissions and confirm the change still supports the workflow.
When reviewing a pull request, trace the change from the resource to its users and data. Ask which accounts, services, or networks can reach it, whether encryption and logging settings remain appropriate, and whether the change crosses into production. For a database, check whether network rules and backup settings match its importance. For an identity change, ask what the role can do and which workloads can assume it.
These checks are most useful when the proposal explains the reason for the change. “Allow the report worker to read the invoice queue” gives a reviewer a concrete claim to compare with the permissions. “Fix cloud access” does not. Clear context helps people catch a mismatch without guessing what the author intended.
Use automated checks to catch patterns, then apply human judgment
Automated checks catch repeatable problems, while reviewers judge context and intent. Formatting and validation checks can find malformed configuration or unsupported fields. Security scanners and policy-as-code rules can flag known risky patterns, such as a public access setting that violates team policy. A passing result does not prove that a change is safe for a particular service.
Imagine a scanner flags a network rule that allows access from a broad range. The alert deserves attention, but the reviewer still needs to learn whether the rule is temporary, limited to an isolated test environment, or attached to a public production service. The same pattern can carry different risk in different settings. Conversely, a scanner may miss a dangerous combination of individually acceptable settings.
A useful workflow runs checks on proposed changes and makes their results visible beside the code and plan. Reviewers can then focus on the flagged resources and the parts that need domain knowledge. Keep the checks focused: a flood of irrelevant alerts teaches people to click through them. Teams should tune policies as services and cloud platforms change, and record why a high-risk exception exists.
AI-assisted generation makes review just as necessary. A tool may draft a working configuration quickly, but it can still make assumptions about provider behavior, existing resources, or permissions. Treat generated IaC like a first draft: check what it declares, inspect the plan, and confirm that the result fits the real environment before anyone applies it.
Review shared modules and dependencies for their wider effects
Review shared modules and dependencies for every environment they can affect. A reusable module can make infrastructure consistent, but one change to its defaults may reach many applications or accounts. The change author and reviewer should check who calls the module, which versions they use, and whether the new behavior fits existing environments.
For example, a platform team updates a shared module so newly created services use a stronger logging setting. That change may help future services, yet it could also require permissions or storage that older callers do not have. A reviewer can ask which callers inherit the default, whether the update changes existing resources, and how teams will learn about a compatibility requirement.
Version pinning helps make those effects easier to reason about. If a dependency can change without a reviewed version update, a plan may behave differently from what the team last examined. Pinning a known version creates a visible point of change; updating it deliberately gives reviewers a chance to inspect new defaults and provider behavior.
Keep shared-module pull requests small and describe their callers. A short note naming the affected environments, expected plan changes, and migration steps gives the next team a useful trail. When a shared change is too broad to understand in one review, split it into a behavior change and a separate rollout. That makes both the decision and any unexpected effect easier to trace.
Keep state, secrets, and manual changes in the review picture
Review state access, secret handling, and infrastructure drift because they affect what a plan can reveal and how accurately it represents the running system. State files can contain sensitive values or details about deployed resources, so restrict access and store them using the IaC tool’s recommended protections. Do not commit secrets to configuration or paste them into review comments.
Consider an engineer changing a production firewall rule directly during an incident. The service recovers, but the declared configuration still describes the old rule. Later, a plan may propose restoring the previous setting or show unexpected changes because the running environment and code differ. Recording the emergency change and updating IaC promptly helps the team regain a reliable view of the system.
Drift is the gap between declared configuration and deployed infrastructure. It can arise from manual edits, provider changes, or another process changing a resource. Drift matters during review because the plan reflects the current state as well as the proposed code; a reviewer needs to know whether an unexpected action comes from the pull request or from an earlier change outside it.
Protect the review trail as well as the files. Use limited deployment credentials, protected production environments, and audit logs so approvals connect to actual changes. For emergency fixes, document who authorized the expedited path, then review and record the change promptly. This keeps a fast response from becoming a permanent blind spot.
Make review depth match the change’s potential impact
Scale review to the change’s reach and impact so high-risk work gets careful attention while routine updates remain manageable. Production identity, network, and data changes generally deserve more scrutiny than a low-risk development setting. The right process depends on what a resource supports, who can access it, and how hard it would be to recover if the change failed.
A development label does not always mean low risk. A test environment might hold copied customer data or share a network with production services. Likewise, a small change to a central identity module may affect dozens of workloads. Review the actual connections and data flows instead of relying on the filename or the number of changed lines.
Use a predictable review sequence to focus attention:
- Confirm the intent. Read the pull request description and check that the proposed resources support that goal.
- Inspect the plan. Find creates, updates, replacements, deletions, and the account or environment in scope.
- Check the sensitive paths. Review permissions, network access, data handling, and secrets.
- Confirm safeguards. Check automation results, deployment permissions, and any required specialist approval.
- Leave a useful record. Note material assumptions, exceptions, and follow-up work.
This sequence gives a team a shared starting point, not a guarantee that every change fits the same checklist. A central network change may need an operations specialist; a minor development tag update may need only a familiar maintainer. Small, focused changes are easier to inspect and discuss than a pull request that bundles unrelated work.
Frequently Asked Questions
Is passing validation enough to approve an IaC change?
No. Validation checks whether configuration is structurally acceptable, while review checks intent and operational impact. A valid change can still widen permissions or replace a production resource, so inspect the plan and the environment it targets.
What should I check first in an infrastructure plan?
Start with the target account and environment, then look for resource deletions and replacements. After that, inspect changes to identity, network access, and data handling. Those actions can change availability, reach, or exposure even when the source diff looks small.
Can a security scanner replace human review?
No. Scanners can flag known patterns consistently, but they may miss context-dependent risks or raise alerts that do not fit the environment. A reviewer familiar with the system can judge whether a flagged setting is appropriate and spot assumptions a rule cannot see.
Who should review infrastructure changes?
Choose someone who understands the affected service and the change’s operational or security effects. A production identity or network change may need a specialist in addition to the service owner, while a low-impact development update may need a familiar maintainer.
How should teams review a large plan?
Break unrelated work into smaller pull requests, summarize the high-impact resources, and use policy checks to surface known risks. If the plan remains hard to understand, narrow its scope before approval. Review works best when people can connect each action to a clear purpose.
What is infrastructure drift?
Drift is a difference between the declared configuration and the deployed resources, often caused by manual changes. It can make a later plan propose unexpected updates or hide which change caused a mismatch. Record emergency edits and reconcile them with IaC so future reviews have an accurate picture.
Conclusion
Before approving an infrastructure change, understand both what the files say and what the plan will do. Check the target environment, inspect high-impact actions, and ask whether access, networks, and data handling still fit the service. Use automation to focus attention, then rely on people who know the system to judge context.
A cloud plan is a set of instructions standing at the door to a live system. Read it closely before you hand it the keys.