TL;DR

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
GrapheneOS has implemented new security features aimed at preventing data extraction from locked devices. This development enhances user privacy and security, though some technical specifics remain undisclosed.
GrapheneOS has introduced new security protections designed to prevent data extraction from locked devices, marking a significant step in mobile privacy. The update aims to make it more difficult for unauthorized parties to access user data even if they gain physical access to a device, which matters for privacy advocates and security-conscious users.
According to the GrapheneOS team, the new protections include enhancements to the device’s hardware-backed security features and modifications to the operating system’s data handling processes. These measures are intended to thwart forensic tools and unauthorized extraction methods that rely on bypassing lock screens or exploiting software vulnerabilities.
While specific technical details have not been fully disclosed, developers confirmed that the security improvements focus on strengthening encryption and controlling low-level data access, making data recovery significantly more difficult for attackers. The update is part of GrapheneOS’s ongoing commitment to privacy and security, especially for users in high-risk environments.
Implications for User Privacy and Data Security
These enhancements could set new standards for mobile security, especially for users who require robust protection against physical data extraction. It may also influence security practices in the broader Android ecosystem, encouraging other projects to adopt similar measures. For individuals, this means increased confidence that their data remains protected, even if their device is lost or stolen.
Products Worth Considering

Samsung Galaxy Tab S10 FE 128GB Wi-Fi Android Tablet, Blue
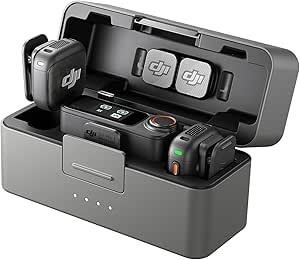
DJI Mic 3 Wireless Microphone System (2 Transmitters, 1 Receiver, Charging Case)

Logitech MX Keys S Wireless Keyboard, Graphite
As an affiliate, we earn on qualifying purchases.
Previous Security Measures and Ongoing Threats
GrapheneOS has long been recognized for its focus on security and privacy, often outperforming stock Android in resisting forensic extraction. Prior to this update, protections included hardware-backed encryption and strict access controls. However, forensic tools and sophisticated attackers have continually evolved, prompting the need for further enhancements.
This development comes amid increasing concerns about physical data extraction attacks, which can bypass standard lock screens through hardware or software exploits. The new protections represent a proactive response to these ongoing threats.
“We have implemented new security measures that significantly raise the bar for data extraction attempts from locked devices.”
— GrapheneOS Developers
Technical Details and Effectiveness Still Under Review
It is not yet clear how effective these new protections are against all types of physical data extraction tools or exploits. The specific technical implementations have not been fully disclosed, and independent testing is ongoing.
Security researchers have yet to verify the resilience of these measures in real-world scenarios, and it remains uncertain whether attackers can find ways around them.
Monitoring and Independent Security Testing Expected Soon
Security experts and researchers will likely conduct tests to evaluate the effectiveness of the new protections. GrapheneOS plans to release further technical details and updates as they become available.
Users and security professionals should stay informed about the evolving security landscape and any additional updates from GrapheneOS.
Key Questions
What specific protections has GrapheneOS added?
GrapheneOS has enhanced hardware-backed encryption and modified data access controls to make data extraction from locked devices more difficult. Specific technical details have not yet been fully disclosed.
Will these protections prevent all forms of data extraction?
It is currently unclear how effective these protections are against all extraction methods. Independent testing and real-world trials are needed to confirm their resilience.
Are these protections available on all devices running GrapheneOS?
These protections are part of the latest updates to GrapheneOS and are intended for devices that support the new security features. Compatibility may vary depending on hardware.
Could attackers bypass these protections in the future?
While the new measures raise the security bar, no system is entirely invulnerable. Attackers may develop new exploits, which is why ongoing security testing is essential.
When will independent testing results be available?
Security researchers are expected to begin testing soon, with results likely emerging within the next few months. GrapheneOS will also release further technical details as they are finalized.
Source: hn