TL;DR

Get privacy and security gear delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
Evidence preservation after a breach safeguards investigation integrity, supports legal action, and helps contain damage. It involves immediate response, forensic imaging, and secure storage, with recent tech advances making it more effective.
Imagine discovering your company’s sensitive data has just been stolen. Your first thought might be to shut everything down and fix the breach. But there’s a critical step often overlooked: preserving evidence. Without it, your ability to investigate, prove fault, or comply with regulations crumbles. Evidence preservation isn’t just about collecting data; it’s about making sure that data remains trustworthy and usable in legal or regulatory settings.
In this guide, you’ll learn what evidence preservation really means after a breach. We’ll explore concrete steps you can take immediately, recent technological advances that make the process easier, and why mishandling evidence can cost you dearly. Whether you’re an incident responder, security manager, or legal professional, understanding these essentials helps you act decisively and confidently when seconds count.
Immediate action is critical: start evidence collection as soon as a breach is detected to prevent data loss or tampering.
Create exact forensic copies of affected systems using trusted tools to maintain evidence integrity.
Maintain a strict chain of custody, documenting every step from collection to storage, to ensure evidence is admissible in court.
Leverage recent advances like AI and cloud forensic tools to speed up evidence collection and analysis.
Failing to properly preserve evidence can invalidate legal cases, increase liability, and hamper breach containment efforts.
Why Evidence Preservation Is the First Line of Defense After a Breach
Evidence preservation is the backbone of effective breach response. When a breach occurs, the clock starts ticking. You need to quickly capture and secure all relevant data—logs, emails, system images, network traffic—before it’s lost or tampered with. Think of it like trying to catch footprints at a crime scene; if you don’t preserve the evidence immediately, it might be wiped, overwritten, or altered.
For example, if an attacker exploited a vulnerability in your web server, the logs showing the attack pattern and the compromised files are crucial. Without preserving these, you risk losing the trail entirely. Proper evidence collection supports internal investigations, helps comply with legal mandates, and strengthens your case if legal action follows. It also prevents further damage by enabling more accurate analysis and faster containment.
In practice, the first response should be to isolate affected systems, but simultaneously, you must start collecting evidence. This dual approach ensures you don’t miss critical data while preventing the attacker from further exploiting your network. Missing this window can mean losing vital clues—like a fingerprint washed away in the rain.
digital evidence forensic imaging tools
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
How to Secure Digital Evidence Without Altering It
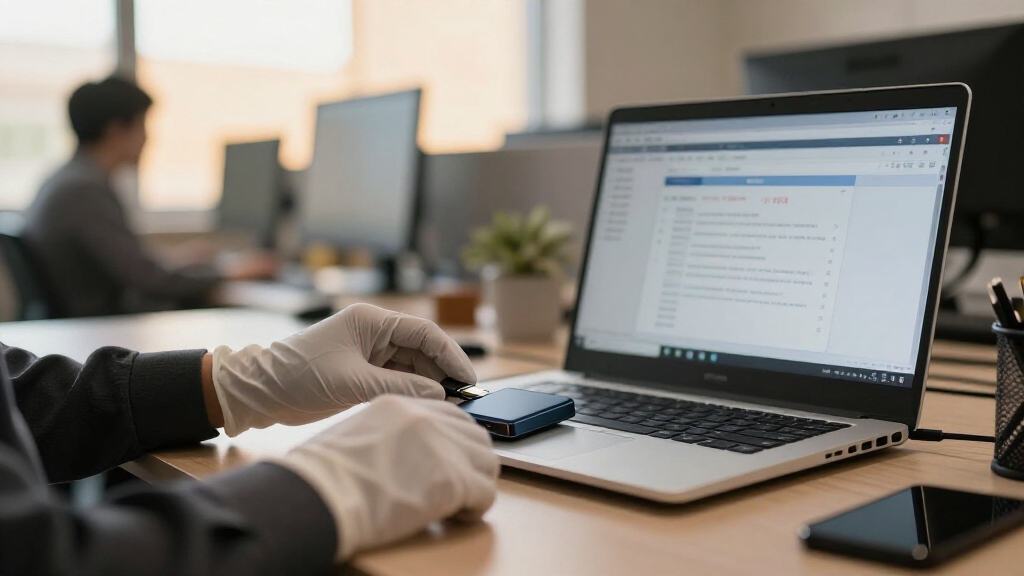
Preserving evidence without changing it is a delicate balancing act. Digital evidence is fragile; even a tiny change can render it useless in court. The gold standard is creating an exact, bit-by-bit copy—called a forensic image—of affected devices and storage media. This process captures everything, including deleted files, slack space, and unallocated sectors, which might contain hidden clues.
For example, imagine copying a compromised hard drive of a server involved in a breach. Using specialized tools like EnCase or FTK, you create a forensic image stored securely elsewhere. This allows analysts to examine the copy without risking the original data. Maintaining the chain of custody—documenting every step from collection to storage—is equally vital. It proves the evidence hasn’t been tampered with.
In practice, limit access to the evidence, store copies in secure, access-controlled environments, and record every action taken. This disciplined approach safeguards the evidence’s integrity, ensuring it remains admissible if the case goes to court. Remember: once evidence is altered, it’s often considered inadmissible, no matter how strong your case.
write-blocker for digital evidence collection
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Recent Tech Advances That Make Evidence Preservation Smarter and Faster
Technology is transforming how organizations preserve evidence after a breach. AI-powered forensic tools now automate much of the collection and analysis, reducing human error and speeding up investigations. For example, AI can scan millions of log entries in seconds, flag suspicious activity, and help prioritize evidence for deeper analysis.
Cloud forensics has also advanced. As more companies store data in cloud environments, preserving evidence involves capturing logs, snapshots, and traffic data directly from cloud providers. This process requires cooperation but is critical for modern breach investigations. Some providers now offer built-in forensic capabilities, making it easier to preserve evidence without risking data loss or tampering.
Standards like NIST guidelines have formalized procedures for evidence handling, ensuring consistency and legal defensibility. Automated tools integrated with SIEM (Security Information and Event Management) and EDR (Endpoint Detection and Response) systems now allow real-time evidence collection, reducing the window for data loss. These technological leaps mean faster, more reliable evidence preservation, even across distributed, remote, or hybrid environments.
As an affiliate, we earn on qualifying purchases.
What Happens if You Fail to Preserve Evidence Properly?
Failing to preserve evidence correctly can have serious consequences. Imagine a company that ignores proper procedures and accidentally overwrites critical logs during a breach response. When the case goes to court, the evidence is considered inadmissible—like trying to prove a crime without a fingerprint. This can doom legal proceedings or regulatory investigations.
For instance, in a recent case, a financial firm lost key logs because they failed to create a forensic image promptly. As a result, they couldn’t prove the attacker’s methods or scope, leading to hefty fines and damage to reputation. Worse, mishandling evidence can suggest negligence, increasing liability and legal penalties.
Beyond legal issues, mishandled evidence hampers your ability to understand the breach, contain it, and prevent future incidents. It’s like trying to piece together a puzzle with missing or damaged pieces. Proper evidence handling isn’t just bureaucratic; it’s essential for effective incident management and safeguarding your organization’s future.
As an affiliate, we earn on qualifying purchases.
Step-by-Step: How to Preserve Evidence During a Breach Response
- Detect and isolate: Identify affected systems quickly. Disconnect compromised servers to prevent further data exfiltration.
- Document everything: Record what’s affected, when, and how. Take screenshots, note timestamps, and log actions.
- Create forensic images: Use trusted tools to clone affected devices, ensuring bit-by-bit copies. Store images securely.
- Collect logs and data: Gather system logs, network traffic captures, emails, and user activity records. Prioritize recent and relevant data.
- Chain of custody: Maintain detailed records of who handled evidence, when, and how. Use secure storage and access controls.
- Analyze and store: Use forensic tools for analysis, then archive evidence in protected environments. Keep copies redundant and secure.
This structured approach ensures that evidence remains trustworthy and legally defensible, providing a clear trail for investigation and legal review. For example, during a ransomware attack, following these steps allowed the security team to prove the attacker’s entry point and timeline, aiding recovery and legal action.
How to Handle Cloud Evidence Without Losing Its Trustworthiness
Preserving evidence stored in the cloud requires special care. Cloud environments are dynamic, and data can be overwritten or lost if not handled properly. The key is to work closely with cloud providers to create immutable snapshots, logs, and traffic records that can be preserved for investigation.
For example, if a breach involves data stored in AWS, you might use AWS CloudTrail logs, EBS snapshots, and VPC flow logs. These should be captured and stored securely, with timestamps and access controls intact. Some cloud providers now offer built-in forensic tools, making it easier to create tamper-proof evidence sets.
Legal and compliance considerations are critical here. You must document how evidence was collected, who accessed it, and how it’s stored. If you’re dealing with GDPR or HIPAA data, ensure that evidence handling complies with privacy rules. Proper protocols prevent disputes over the authenticity or completeness of cloud evidence, which could otherwise derail investigations or legal proceedings.
Frequently Asked Questions
Why is evidence preservation so important after a breach?
It ensures the integrity of data for investigation, legal proceedings, and compliance. Without proper preservation, evidence can be lost, tampered with, or rendered inadmissible, weakening your case and response efforts.What are the first steps to take if I discover a breach?
Immediately isolate affected systems to contain the breach, then document everything—what systems are affected, when, and how. Start creating forensic images and collecting logs while maintaining a detailed record of all actions taken.How do I keep evidence unaltered during collection?
Use trusted forensic tools to make exact copies of affected media, limit access to evidence, and document every step in a chain of custody. Store evidence securely to prevent tampering or accidental modification.Can cloud-stored evidence be preserved effectively?
Yes, but it requires cooperation with cloud providers to capture immutable snapshots, logs, and traffic data. Following established protocols and documenting the process ensures the evidence remains trustworthy and legally defensible.How long should evidence be kept after a breach?
Retention periods depend on legal requirements, organizational policies, and the breach’s nature. Usually, evidence should be retained at least until legal or regulatory obligations are fulfilled, often several years.Conclusion
Preserving evidence after a breach isn’t just a technical task; it’s a strategic necessity. Clear procedures, the right tools, and awareness of recent innovations turn a chaotic response into a controlled investigation. Think of evidence preservation as laying a solid foundation—without it, the entire structure of your response and legal standing crumbles.
When seconds count, having a well-practiced, concrete plan for evidence preservation makes all the difference. It helps you act swiftly, protect your organization, and stand firm in legal and regulatory battles. In a digital world where data is everything, safeguarding your evidence is safeguarding your future.
Halloween Picks
halloween
As an affiliate, we earn on qualifying purchases.