TL;DR

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
An IPinfo analysis found 1,331 internet-accessible Danfoss refrigeration dashboards in France before attacks on supermarket cooling systems on Oct. 11–12, 2026. It reported that 85% of those dashboards ran software with known flaws, but the attacker, entry method and link between the exposed dashboards and each attack have not been established publicly.
Hundreds of French supermarkets reported attacks on refrigeration systems on Oct. 11–12, 2026, while an analysis of internet scans by IPinfo found that 1,331 Danfoss control dashboards in France were exposed online before the incidents. IPinfo said 85% of the French dashboards ran software with known security flaws; authorities have not publicly identified the attackers or confirmed how they gained access.
IPinfo said its scan on Oct. 6–7, five days before the attacks, found 2,528 internet-accessible Danfoss StoreView dashboards worldwide. France accounted for 1,331, or 53%, more than the 1,197 found across 72 other countries and territories combined. Poland had the next-highest count, at 179, followed by the United States with 101.
The company reported that 1,136 French dashboards ran software with known flaws. That included 527 older controllers no longer supported by Danfoss, 280 systems missing 2023 security fixes and 329 missing 2025 fixes. IPinfo said 195 dashboards had all known fixes. These counts describe systems visible in its scans, not proof that every device was compromised or involved in the attacks.
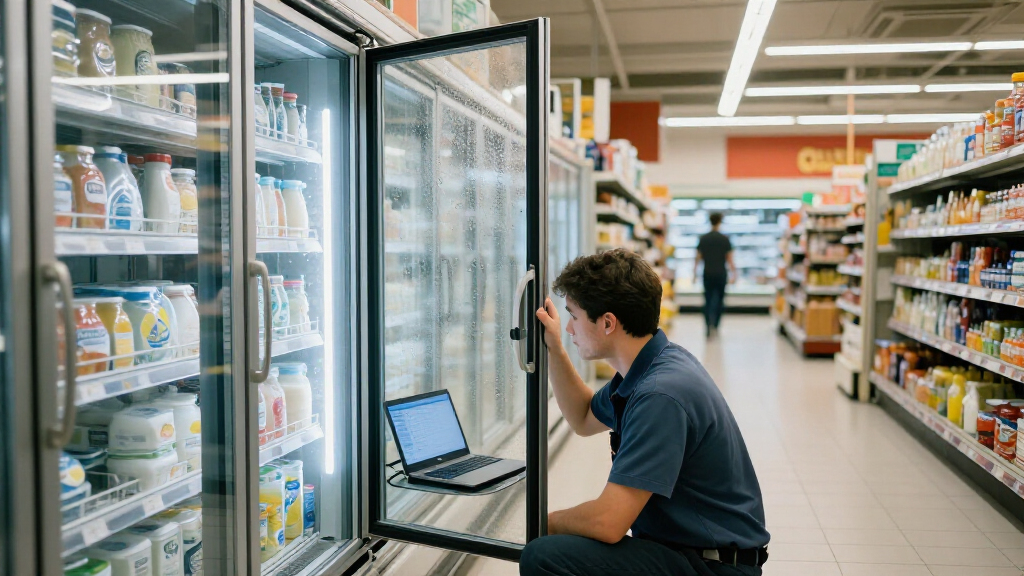
The attacks reportedly put some refrigeration equipment into defrost mode, a process that warms cooling components to melt ice. The Paris prosecutor said some units reached 50°C (122°F) and some equipment began to catch fire, according to IPinfo’s report. Retailers discarded fresh and frozen food. Futura-Sciences reported that more than 400 stores were affected, with losses potentially reaching several million euros.
Why Exposed Cooling Controls Matter
Supermarket refrigeration is a physical service with direct consequences for food safety, store operations and equipment. The reported incidents show how online access to industrial control systems can create risks beyond stolen data or interrupted office networks: a change to equipment settings can affect temperature-sensitive stock and may damage machinery.
The scale of the exposure is also relevant. France had more visible dashboards than all the other countries in IPinfo’s scan combined, while the share running flawed software was close to the share elsewhere. IPinfo’s figures suggest that France stood out mainly in the number of systems online, not because its systems had a higher measured rate of outdated software. The scan cannot establish why so many were reachable or whether exposure caused the attacks.
Keeping remote access may serve a business purpose. The report said refrigeration contractors or head offices use connections to monitor and service equipment. CERT-FR advised operators to restrict access or disconnect controllers, while also telling them to check insurance terms before cutting data links used by contractors. That tension makes the issue a practical security and operations problem, not simply a matter of installing updates.
hardware security keys for online accounts
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Months of Visible Dashboard Exposure
IPinfo said its weekly scans found roughly 2,464 to 2,622 Danfoss dashboards online in each scan from late March 2026 until the attacks. Of the 1,331 French dashboards seen before the incidents, 1,019 were at the same internet addresses on March 30. IPinfo said the share of French systems fully updated increased from 14% to 24% over that period.
The dashboards let stores and technicians monitor and manage refrigeration controllers. IPinfo described them as web control panels that could be opened by someone who knew the address. The analysis found that nearly all of the French systems were on telecom networks rather than in data centers or cloud services. It said two-thirds used one national provider, but did not establish why this pattern was concentrated in France.
Danfoss told IPinfo that most affected equipment was legacy hardware, naming the AK-SM 800 and AK-SC 355. Danfoss declared the AK-SM 800 end of life in 2023. IPinfo also cited a security firm’s 2023 publication of a login bypass affecting that controller and said Danfoss advised restricting network access. Newer AK-SM 800A units could also be out of date: IPinfo’s version analysis identified missing fixes for vulnerabilities disclosed in 2023 and 2025.
“Most of the affected equipment was legacy.”
— Danfoss, as quoted by IPinfo
industrial control system security devices
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Attack Method and Scope Remain Unknown
No attacker has been publicly identified, and authorities have not announced how the systems were accessed. The Paris prosecutor’s office opened an investigation, but the source material does not provide its findings or establish that the exposed dashboards were the route used in every incident.
The reported store totals vary by retailer and source. Carrefour said 80 stores were hit; Intermarché and Netto together reported more than 300; Monoprix said about 5% of its stores were affected. Leclerc and Coopérative U also confirmed attacks, with Schelcher citing 80 affected U stores out of 2,000. These statements do not amount to a final national count, and the estimated losses remain provisional.
IPinfo said most of the dashboards it had observed went offline after the attacks, but 316 of the 1,331 French dashboards were still online on Oct. 14. The scans show internet visibility, not whether a system was vulnerable in the same way, accessed by an attacker or responsible for a particular store’s disruption.
cybersecurity for supermarket refrigeration
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Investigation and Network Changes
The Paris prosecutor’s investigation is the next public route to answers about who was responsible and how access was obtained. CERT-FR said attack campaigns were probably still ongoing in an alert updated Oct. 13. The agency expanded its notice to include XWEB monitoring systems from Copeland and its Dixell brand, as well as Danfoss controllers.
Operators were advised to disconnect the systems or limit who can connect to them. IPinfo’s Oct. 14 scan indicates that many dashboards were no longer visible after the attacks, but it also found hundreds still online. The supplied reporting does not say whether retailers completed access restrictions, installed all available fixes or restored affected equipment and stock.
Further updates from prosecutors, CERT-FR, retailers and equipment suppliers may clarify the number of affected sites and the extent of losses. Until then, the exposure data should be read as a measure of systems visible online before and after the incidents—not as a confirmed count of compromised controllers.
As an affiliate, we earn on qualifying purchases.
Key Questions
What happened to French supermarket refrigeration systems?
Retailers reported attacks on Oct. 11–12, 2026. IPinfo said some refrigeration systems were pushed into defrost mode, warming equipment and leading stores to discard fresh and frozen food.
How many dashboards did IPinfo find exposed in France?
IPinfo found 1,331 Danfoss StoreView dashboards reachable online in France in a scan on Oct. 6–7. That was 53% of the 2,528 dashboards it found worldwide in that scan.
Does the scan prove those dashboards were hacked?
No. The scan recorded dashboards accessible from the internet and assessed software versions. It does not prove that each system was compromised or that exposed dashboards were the route used in the attacks.
What did authorities advise operators to do?
CERT-FR advised operators to disconnect affected controllers or restrict access. It also told them to check insurance terms before cutting data links used by refrigeration contractors.
Who carried out the attacks?
The attacker and the method of entry have not been publicly identified in the supplied reporting. The Paris prosecutor’s office opened an investigation.
Source: hn
Halloween Picks
halloween
As an affiliate, we earn on qualifying purchases.