TL;DR

Get privacy and security gear delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
Device trust means an organization considers a device’s identity, management, security condition, and request context when deciding whether to grant access. A policy may allow a managed, up-to-date laptop, ask for more verification from an unfamiliar device, or limit access from a personal phone. Passing a device check is useful evidence at that moment, not a permanent guarantee that the device or user is safe.
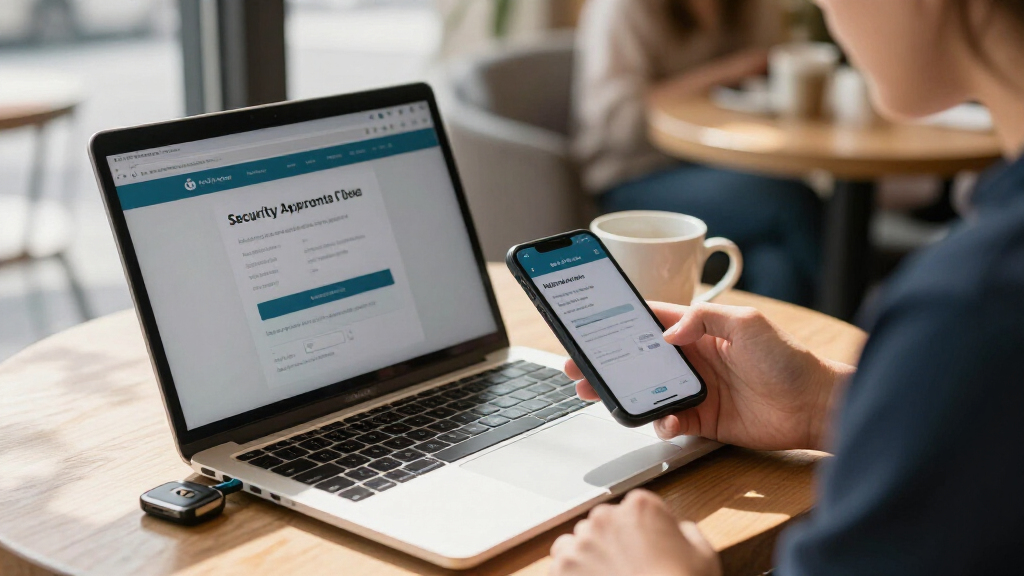
Your password can be correct while the laptop in front of you is missing a security update. That gap matters: user authentication tells an organization something about who is signing in, while device trust tells it something about the device making the request.
When an organization decides whether to grant access, it can consider the device’s identity, ownership, security condition, and the sensitivity of the requested service or data. A managed laptop might open a work document straight away; an unfamiliar phone might need an extra check or receive access to fewer features.
This guide explains what device trust means in access decisions, how organizations use it, and what a failed check can mean for you. You’ll also see why “trusted” describes a device’s fit with a policy at a particular time, not a promise that nothing can go wrong.
Device trust adds evidence about a device’s identity, management, and security condition to an access decision.
A valid password or passkey does not by itself show that a device is managed, current, or encrypted.
The same personal device may be allowed to view low-risk information and blocked from downloading sensitive files.
A failed check can mean a policy requirement was not met; read the message and ask IT for the specific fix.
Device status can change, and a passing check is not a permanent guarantee about the device or the person using it.
What Device Trust Means in Access Decisions
Device trust adds evidence about the device behind a sign-in: its identity, management, security condition, and the request it is making. It helps an organization choose an appropriate access response. A passing check describes a moment in time; it is not a permanent guarantee that a device or user is safe.
What a device check can tell an organization
Device trust brings several kinds of evidence into an access policy. A signal only helps when it is reliable, current, and tied to the device making the request.
Device identity
Enrollment or a certificate can help link a request to a known device.
Ownership & management
Is it organization-owned, personally owned, or unmanaged? What controls can be applied?
Security posture
Policies may check supported operating systems, updates, encryption, screen locks, endpoint protection, or jailbreak and root status.
Request context
The user, application, data sensitivity, location, and network can all shape the decision.
Policy response
Rules translate evidence into an outcome: allow, limit, deny, request stronger verification, or guide remediation.
Signals can change
A device may fall out of compliance after a session begins. Some policies reevaluate conditions over time.
A correct sign-in is not a device health report
Your password or passkey provides evidence about authentication. It does not by itself show that your laptop is managed, encrypted, updated, or in a condition the organization accepts.
Is this the right user?
A password, passkey, or authenticated session helps establish who is signing in and how the sign-in was verified.
Does this device meet policy?
Management and posture signals can show whether the device meets requirements for this particular request.
The same device can get different outcomes
Policies can match the access level to both device condition and the sensitivity of the resource. This makes device trust a decision about a request, rather than a permanent label attached to a device.
| Request example | Device evidence | Possible policy outcome |
|---|---|---|
| Open a staff directory | Personal phone; limited management | Allow view |
| View a work calendar | Unfamiliar device; sign-in verified | Ask for more verification |
| Download confidential files | Unmanaged device; posture unknown | Limit or block download |
| Open payroll records | Managed laptop; current and encrypted | Allow under policy |
How organizations turn checks into access decisions
Device-management platforms, certificates, endpoint security tools, or identity-provider integrations can supply signals. The implementation varies; policy determines what happens next.
Connect the request to a device.
Check management and security posture.
Consider the app, data, user, and request.
Match evidence to access requirements.
Allow, limit, verify, deny, or remediate.
Why an access prompt may appear
Imagine a designer opening a shared project folder. The decision can change with the device and the action requested—even when the account is the same.
Edit files
Enrolled, updated, and encrypted; it meets the organization’s requirements for editing.
Edit allowedView a limited version
It can reach a browser view, while downloading the same project files stays restricted.
Limited accessCheck not met
The device cannot satisfy a required policy condition; the message points to an approved device.
Use approved deviceTrust is contextual—and can change
Zero-trust approaches evaluate a request using available context instead of assuming it is safe because it comes from inside an office network. A compliant device is one part of that evaluation.
A failed check is not a diagnosis.
It may mean a policy requirement was not met, or that the available signal was missing or out of date. Read the message and ask IT for the specific fix. A passing check is useful evidence at that moment, not proof that nothing can go wrong later.
Keep the questions distinct
Identity, device condition, and resource sensitivity work together to shape a practical access outcome.
What device trust tells an organization before it grants access
Device trust is the role a device’s identity, ownership, security condition, and request context play when an organization decides whether to grant access. It gives the access policy evidence about the laptop, phone, or tablet behind a sign-in. It does not establish that the person using the device is legitimate or that the device is completely safe.
Think of a badge reader at an office door. Your badge identifies you, but a guard may still check whether you are entering a restricted room. Digital access works in a similar way: identity answers who is signing in, while device checks help answer whether this device meets the requirements for this request.
For example, Maya signs in to her company account with a valid password and a passkey from her managed laptop. The organization may also check whether the laptop is enrolled in management, encrypted, and up to date. If Maya later signs in from an unknown tablet, the same account credentials do not make that tablet meet the company’s device requirements.
That distinction is useful for everyday access. A device may meet policy for a low-risk service, such as viewing a public staff directory, but fail the checks needed to download payroll records. Trust depends on the request, so it is better understood as a policy decision about access than a permanent label attached to a device.
device management security software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Which device checks can change your access
Device trust can draw on several kinds of information: whether the device can be identified, who owns or manages it, whether it meets security requirements, and what the user is trying to reach. These checks help an organization tailor access to a particular request. A check only helps if its signal is reasonably reliable and current.
A work laptop enrolled with the organization might report that its operating system is current and its storage is encrypted. A personal phone may have a screen lock but no organization management. Those devices can receive different access because the organization has different ways to verify and control them.
Here are common signals an access policy may use:
- Device identity: Is the device enrolled, or can it present a certificate that links it to a known device?
- Ownership and management: Is it company-owned, personally owned, or unmanaged, and what controls can the organization apply?
- Security posture: Is the operating system supported, are important updates installed, is storage encrypted, and is a screen lock enabled?
- Request context: Which user, app, data, location, and network are involved?
- Policy response: Should the request be allowed, blocked, limited, or require another authentication step?
For instance, a company may let a contractor read meeting notes on an unmanaged tablet but prevent downloads of confidential plans. That arrangement treats device condition and data sensitivity as parts of the same decision, while avoiding an all-or-nothing response to every personal device.
As an affiliate, we earn on qualifying purchases.
Why a valid sign-in may still get a device check
Device trust adds information that a password or authenticated session cannot provide: whether the device appears managed, updated, encrypted, and in a condition the organization accepts. A valid sign-in is evidence about authentication; it is not a health report for the laptop or phone. Access policies may use both kinds of evidence together.
Imagine you sign in to work email on your usual laptop, then leave it open in a café while you step away. Your sign-in may still be valid, but a screen lock and other device controls reduce what someone else can do if they reach the machine. In a different scenario, a phone with an outdated operating system may expose work data to risks that the password check never evaluated.
Authentication methods such as passkeys can make it harder for someone to impersonate you with a stolen password. They still do not show whether the device has the latest security updates or whether an organization manages it. Strong authentication and device checks answer different questions, so organizations can require both for sensitive services.
A policy might let you read an ordinary calendar after a familiar sign-in, ask for an extra verification step before accessing a finance system from a new device, or block access from a device missing a required security control. The practical effect is a more tailored decision. For you, a prompt or access limit can be a sign that the request fell outside policy, rather than proof that your account has been taken over.
As an affiliate, we earn on qualifying purchases.
How organizations turn device signals into access outcomes
Device trust becomes useful when an organization connects device signals to clear rules about what happens next. Depending on the application and the information involved, the policy can allow access, ask for stronger authentication, limit what a person can do, deny the request, or explain how to fix a device problem.
Consider a designer trying to open a shared project folder from three devices. Her managed work laptop meets the organization’s update and encryption requirements, so she can edit files. Her personal phone can open a limited browser view, but it cannot download the same files. An unfamiliar tablet fails a required check and receives a message explaining which approved device to use.
That kind of decision reflects a broader idea associated with zero-trust access: a request is evaluated using available context rather than assumed safe because it comes from inside an office network. Organizations may use device-management platforms, certificates, endpoint security tools, or identity-provider integrations to collect signals. The details vary, and the label alone tells you little about how well a particular check works.
Policies can also change access after a session begins. If a device becomes noncompliant or a high-risk signal appears, the organization may ask you to sign in again, restrict the session, or revoke access. For example, an update that disables required encryption could affect access the next time the device is checked. A device’s status can change, so a decision made earlier does not have to hold forever.
As an affiliate, we earn on qualifying purchases.
How the same device can get different access
Device trust is a decision tied to the user, device, request, and policy—not a universal pass or fail sticker. The same device may be acceptable for one task but not another because the data carries a different level of risk or the organization can apply different safeguards.
For example, a personal phone might be allowed to show a work calendar through a browser, while the organization blocks attachments from being saved to the phone. On a managed laptop, the user might be able to edit those same attachments. That distinction can let people use personal devices for practical tasks while keeping more sensitive information behind stronger controls.
A simple comparison makes the choices clearer:
| Request | Possible device evidence | Possible policy result |
|---|---|---|
| View a staff directory | Successful sign-in; device not managed | Allow read-only access |
| Open sensitive financial records | Managed device; encryption and updates meet policy | Allow access, possibly with stronger authentication |
| Download confidential files | Personal device without required controls | Limit downloads or direct user to an approved device |
| Use an app from a device failing a required check | Outdated operating system or unknown device identity | Block access and explain remediation |
These outcomes are examples, not fixed rules. An organization chooses policies based on its systems, the sensitivity of the data, and what it can reliably check. Limited access can be a useful middle ground when full access would call for controls a personal device does not have.
What a failed device check means—and what you can do
A failed device check means the request did not meet one or more policy requirements at that time. The organization may block the request, limit access, ask for more verification, or guide you through a fix. It does not automatically mean your device is infected or that someone has stolen your account.
Suppose you receive a message saying your work laptop is out of compliance just before a video call. A missing operating system update, expired device certificate, disabled screen lock, or stale management report could explain the result. Your organization’s support team can tell you which check failed and whether you need to update, reconnect the device to management, or use another approved option.
If access stops working, take these practical steps:
- Read the message carefully. Note the app, device, and requirement it names.
- Use the organization’s approved fix. Install an update or reconnect to management only through the normal support process.
- Contact IT if the reason is unclear. Share the error wording and device type; avoid sending passwords or passkeys.
- Ask about a permitted alternative. A managed computer, browser-only session, or limited-access path may meet your need.
For example, a traveling employee whose laptop missed a required update may be able to use a managed loaner while IT helps restore compliance. A clear recovery path matters: security rules work better when people can understand and meet them, especially when access is needed to do ordinary work.
Where device trust has limits and deserves a careful setup
Device trust has limits because a compliance signal only describes the checks an organization can see, and those checks can become outdated. A device that passed a check yesterday could be lost today, develop a problem, or fall behind on updates. A compliant device also does not prove that the person holding it is the account owner.
Picture a laptop that shows a green compliance status but gets stolen from a car. The earlier status does not prevent someone from physically possessing it. Strong authentication, screen locks, data protection, and timely access changes still matter. Similarly, a device with current software can be used by someone who has obtained the account holder’s credentials through another route.
Organizations also need to respect privacy. A personal phone may hold family photos, messages, and location history beside a work calendar. Before applying checks, a responsible organization should explain what information it collects, how it uses that information, what happens when checks fail, and how users can get help. It should collect only information that supports the access decision.
Stale or weakly verified status can lead to the wrong result in either direction: a device may be blocked despite meeting requirements, or allowed based on information that no longer reflects its condition. Clear support instructions and regular evaluation help users resolve errors. “Trusted” means the device met defined requirements for a request; it should never be read as “permanently safe.”
Frequently Asked Questions
Does device trust mean my device is completely secure?
No. It means the device met defined checks at a particular time, and those checks may not cover every risk. A device can become lost, compromised, or out of date after it passes.
Is device trust the same as user authentication?
No. Authentication provides evidence about who is signing in; device trust assesses characteristics of the device making the request. An organization may require both before it grants access to sensitive information.
Can an organization trust my personal phone?
Sometimes, depending on its policy and the information you need. It may allow limited browser access, require selected device controls, or block downloads while allowing you to view basic work information.
Does a VPN make a device trusted?
No. A VPN can provide a protected network connection, but it does not prove that a device is managed, up to date, encrypted, or free of compromise. An organization may consider network context alongside device checks.
What should I do when my device fails a check?
Read the access message for the named requirement and follow your organization’s approved fix. If it is unclear, contact IT with the error wording and device type; ask whether a managed device or limited-access option is available.
Can a trusted device still be used in an attack?
Yes. A stolen device, compromised account, or newly discovered vulnerability can undermine earlier checks. Device trust works best as one part of a set of access protections, not as proof that a request is harmless.
Conclusion
When you see a device check, read it as one piece of evidence in an access decision. Authentication identifies a sign-in; device trust describes whether the device fits the request’s policy. If a check blocks you, find out which requirement failed and use the approved fix or access alternative.
A green status is a snapshot, like a clear dashboard on a car: useful to see, but no substitute for paying attention to what happens next.
Halloween Picks
halloween
As an affiliate, we earn on qualifying purchases.