TL;DR

Get privacy and security gear delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Plan hardware purchases around the people, places, and information each device must support. Set testable security and update requirements before comparing models, verify vendor and management claims, and budget for secure operation through retirement. A device is a sound purchase only if your organization can protect and manage it for its full useful life.
A laptop can look new on Monday and become a security headache years before its casing wears out. If the vendor stops providing firmware fixes, or your IT team cannot manage its encryption, that bargain device may cost more than its price tag suggests.
When you plan hardware purchases around security requirements, you start with how people will use each device, what information it will touch, and how long you can support it. Then you compare products against clear, verifiable needs: updates, authentication, management, and safe retirement.
This guide gives you a practical way to make those decisions. You will see how to write requirements, weigh vendors and costs, and build a lifecycle plan that fits real work—from a shared reception laptop to a machine that administers company systems.
Map each device to its user, location, data, and access before selecting hardware.
Write requirements as behaviors you can verify, such as centrally managed encryption with hardware-protected keys.
Check documented firmware and security support dates, then plan replacement before support ends.
Test enrollment, updates, access revocation, repair handling, and retirement with the tools your team uses.
Compare usability and total operating cost alongside security; a control that disrupts work may be bypassed.
Procurement field guide / Security by design
How to Plan Hardware Purchases Around Security Requirements
Start with the people, places, and information each device must support. Set testable security and update requirements before comparing models, then budget for secure operation through retirement.
Match protection to real use
A shared reception laptop, an accounting workstation, and an infrastructure admin machine face different risks. Map the work before you choose the model.
Who uses it, and where?
Record the user or role, travel pattern, physical exposure, accessibility needs, and support environment.
What will it touch?
Identify sensitive records, local files, cloud services, identity systems, and the device’s network connections.
What can it control?
Separate routine work from sensitive information, privileged access, and exposed environments to set sensible security tiers.
Make requirements verifiable
Feature names can hide important gaps. State the behavior needed, how it will be checked, and what evidence procurement must retain.
Describe a realistic risk
Example: a lost laptop could expose locally saved payroll or customer records.
Name the needed behavior
Require full-disk encryption, hardware-backed key protection, and central management.
Define the proof
Check product documentation, configuration tests, or an agreed procurement standard.
Record a decision
Score pass, fail, or documented exception. Keep evidence with the purchasing record.
Secure Boot · TPM or equivalent · firmware protection and secure updates · biometric or security-key authentication · endpoint detection and device management compatibility · physical privacy controls where appropriate.
Look beyond the sticker price
Ask how long operating-system and firmware fixes will be available, how updates arrive, and what happens when components reach end of support.
| Review area | Ask for | Verify with |
|---|---|---|
| Update lifecycle | Documented security support dates and firmware delivery method | Vendor commitment; update test |
| Management | Enrollment, policy control, monitoring, and patch compatibility | Your identity and endpoint tools |
| Vendor practice | Disclosure process, update history, and component transparency | Documentation; independent review as risk warrants |
| Supply chain | Approved sourcing and provenance records for higher-risk fleets | Reseller and procurement records |
| Operations | Warranty, repair, accessories, licenses, staff time, and disposal | Lifecycle cost estimate |
Budget for the whole useful life
A lower upfront price can hide short support, manual maintenance, or early replacement. Compare all material costs against the planned support window.
Lifecycle cost lens
Illustrative cost categories, not market price data. Include staff time: repeated manual firmware work also has a real cost.
Support window decision
Confirm support covers the intended service life. Schedule a review ahead of the documented end date so there is time to migrate, replace, repurpose, or retire devices.
Assign owners from setup to retirement
A secure purchase needs a working operational path. Confirm who owns each step and how completion will be checked.
Provision
Secure setup
Track
Inventory & owner
Maintain
Patch & firmware
Respond
Repair, loan, loss
Review
Support end date
Retire
Wipe, reuse, dispose
Security has to work for the people using the device.
Balance protection with usability, accessibility, performance, battery life, and repairability. Controls that disrupt work may be bypassed. Pilot enrollment, updates, access revocation, repair handling, and retirement with the tools your team actually uses before scaling the purchase.
Start with the person, place, and data behind each device
Plan hardware purchases around the work each device must do: identify its user, location, information, and connections before you choose a model. Those details show which risks matter and how much protection the device needs. A laptop that stays in a locked office and handles public documents has a different job from one used in airports to access sensitive records.
Take a small accounting team as an example. Staff may work from home, share spreadsheets containing payroll details, and connect through cloud services. Theft, unauthorized access, and weak update practices deserve attention. A device used by a network administrator also needs controls appropriate to its powerful access, even if it never stores customer files locally.
Write down realistic threats such as loss, malicious software, unauthorized access, supply-chain compromise, and unsupported software. Then connect each threat to a business consequence: a stolen laptop could expose saved files, while an unpatched firmware issue could undermine protections below the operating system. This is how hardware choices shape risk over time.
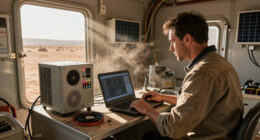
Ask what the device will touch and where it will travel. A field technician working beside dusty equipment may need a repairable, durable model and a reliable way to connect securely from outside the office. A desk-based employee may care more about accessibility, a webcam shutter, and compatibility with centrally managed login tools.
Do not give every user the same security tier just to simplify a spreadsheet. Start with a basic role map: routine work, sensitive information, privileged access, or exposed environments. That map gives your team a reason for each requirement and a sensible answer when someone asks whether a more secure model is worth the added cost.
business laptop with hardware encryption
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Turn security needs into requirements you can actually verify
- Describe the risk. For example, a lost laptop could expose local customer records.
- Name the needed behavior. Require full-disk encryption with keys protected by hardware and managed centrally.
- Check how you will verify it. Use product documentation, configuration tests, or an agreed procurement standard.
Clear requirements make a purchasing decision easier to defend and compare. “Must support encryption” sounds useful, but it leaves open whether encryption can be switched on centrally, whether the keys receive hardware protection, and how IT can check that coverage. Spell out the behavior your team needs instead of relying on a feature name.
Depending on the role, your criteria may include Secure Boot, a TPM or equivalent for hardware-backed key storage, firmware protections, biometric or security-key authentication, and compatibility with device management and endpoint detection tools. A physical camera shutter may make sense for a room used for confidential calls. No checklist fits every organization, so link each item to a use case.
For example, a laptop used to administer company infrastructure should support centrally managed encryption and strong authentication. If your identity platform uses hardware security keys, test that a proposed model supports them in the way your staff will actually use them. A specification that can be checked before purchase saves surprises during rollout.
Use a simple scorecard with a pass, fail, or documented exception for each requirement. Ask for evidence, such as written update commitments or compatibility documentation, rather than accepting a sales description as proof. That creates a clear record for procurement and helps IT explain why a device was chosen or rejected.
enterprise device management software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Compare update support before you compare sticker prices
A device is a sound security purchase only if it can receive fixes for as long as you plan to use it. Ask the vendor how long operating-system and firmware security updates will be available, how those updates arrive, and what happens when a component reaches end of support. Put the answer beside the price; a low upfront cost can hide a short support window.
Imagine two laptops that each meet your basic requirements. One costs less but has an unclear update commitment, while the other costs more and comes with documented support that matches your planned replacement cycle. The cheaper model may need early replacement or create extra review work. The right answer depends on the support evidence and the sensitivity of the work, not the number on the receipt.
Include more than purchase price when you plan budgets. Factor in setup, management licenses, warranty, accessories, repair time, software compatibility, and secure disposal. If a fleet of 40 devices needs an extra hour of manual firmware maintenance every month, those hours matter just as surely as a line item from a supplier.
Plan replacement before support ends, with enough time to migrate users and data. A team might schedule a review six months ahead of a model’s documented support end date, then decide whether to replace, repurpose, or retire it. That calendar keeps an aging device from quietly becoming the default because no one budgeted for its successor.
Longer use can help control costs and reduce waste, but only when updates and management remain available. A device that lasts physically for eight years may not be a safe choice for sensitive work if meaningful security support ends much earlier. Treat support duration as part of the product, not a footnote.
secure hardware lifecycle management tools
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Check the vendor and supply chain with evidence
Assess a hardware vendor by checking its security practices, update history, vulnerability-disclosure process, and clarity about product components. These details help you judge whether the company can respond when a flaw appears and explain what buyers should expect. Match the depth of review to the risk: a large deployment handling regulated information calls for more scrutiny than a few low-risk peripherals.
Ask how the vendor publishes fixes, how customers learn about security issues, and where the device and its components come from. For higher-risk purchases, your process may include approved resellers, supplier reviews, or records showing where devices entered your organization. Those steps give you better visibility if a delivery is unexpected or a device needs an investigation later.
Suppose a supplier offers a discounted batch through an unfamiliar channel. The lower price does not tell you whether the units are genuine, supported for your region, or covered by the same warranty. Your procurement team can compare the reseller against approved channels and confirm serial numbers and support terms before deploying the batch.
Verify claims against product documentation, and use independent testing or procurement standards when the stakes justify it. A logo or phrase such as “enterprise grade” does not answer how firmware updates are delivered or how long fixes will continue. Ask for details that map to your requirements, then record the evidence and any gap.
Supplier requirements can vary by industry, contract, and location. Avoid turning broad supply-chain concerns into a one-size-fits-all ban; instead, decide what evidence your organization needs for each risk tier. That keeps the review practical while giving higher-risk deployments stronger traceability.
As an affiliate, we earn on qualifying purchases.
Make sure IT can manage the device after delivery
A secure device must work with the tools and people responsible for enrolling, configuring, monitoring, and patching it. Before a purchase, confirm compatibility with your identity provider, device management platform, endpoint security tools, network controls, and support process. A model that cannot be managed consistently can leave gaps even when its hardware features look strong on paper.
Picture a new hire receiving a laptop that cannot enroll in the company’s management system. IT may have to configure it by hand, miss a standard setting, or delay the employee’s work. That friction affects whether devices receive consistent protections once they leave the purchasing spreadsheet and enter daily use.
Test representative models before ordering at scale. Check that the team can enforce encryption, apply firmware updates, confirm device health, and revoke access when a device is lost or a user leaves. For remote staff, verify that these tasks still work when the laptop is away from the office and connected through ordinary home internet.
A smaller set of approved models often makes support easier. With fewer variations, technicians can maintain tested configurations, keep compatible spare devices, and compare update behavior across the fleet. That does not mean every role must use identical hardware; it means each added model should solve a real need that justifies the extra support work.
Also consider performance, battery life, accessibility, and repairability. If a laptop’s battery cannot last through a field shift, a worker may borrow an unmanaged device or leave it unattended while charging. Security requirements work best when the hardware fits the day a person actually has.
Plan for every handoff, from setup through retirement
Plan security across the device’s full lifecycle: provisioning, ownership tracking, updates, repairs, lost-device response, and secure retirement. A purchase plan should name who owns each task and how the organization checks that it happened. Without that ownership, even a capable device can slip out of sight after a repair or employee handoff.
Consider a laptop sent away for a warranty repair. Before it leaves the office, your process should account for sensitive data, confirm what the repair provider may access, and track the device’s return. If staff receive a loaner, that device needs enrollment and a clear return path too. A simple asset record can connect the serial number, assigned user, status, and support dates.
Use this lifecycle sequence to close common gaps:
- Provision securely: enroll the device, apply approved settings, and confirm encryption.
- Track ownership: record the user, asset identifier, and support dates.
- Maintain it: monitor operating-system and firmware updates.
- Handle changes: account for repairs, loaners, returns, and lost-device reports.
- Retire it safely: remove access, erase storage, and document reuse, recycling, or destruction.
When a device is lost, staff should know how to report it and IT should be able to revoke access promptly. At retirement, remove the device from management and identity systems, erase storage, and confirm it no longer holds organizational data before reuse or disposal. A documented handoff prevents a retired laptop from quietly reappearing with access it should no longer have.
These responsibilities also matter for bring-your-own-device programs. Set enrollment rules, separate work and personal information where possible, and limit access if the organization cannot verify required protections. A personal phone might be fine for email under clear controls, while access to sensitive records may call for a managed device.
Balance strong protections with a device people can use
Choose controls people can follow during a normal workday, because security that disrupts essential work may invite workarounds. Weigh protection alongside accessibility, speed, battery life, repair options, and cost. A device should fit its environment and its users, not just pass a technical checklist.
For instance, a warehouse worker may need a screen that stays readable under bright lights and a device that can withstand regular handling. If a security prompt interrupts every few minutes, the worker may delay updates or ask a colleague to sign in. Testing the real workflow can reveal friction before you buy 200 units.
Compare candidates with one scorecard that covers required security behaviors, update support, management compatibility, warranty, and operating cost. Give mandatory protections a pass-or-fail gate, then compare remaining models on usability and cost. This keeps a flashy feature from outweighing something basic, such as an update commitment your organization can verify.
New hardware may advertise processors for AI workloads. Ask whether your team needs those capabilities and how related software handles sensitive information before paying extra. A dedicated processor is not, by itself, a reason to share work data with a new service or expand what the device is allowed to process.
Repairability and longer use can support both budget and sustainability goals, provided the device still receives security fixes and can be managed safely. If a repair extends the useful life by two years but the vendor stops issuing firmware updates next quarter, the extension may not suit sensitive work. Let the job, support evidence, and people using the device shape the final call.
A device earns its place in your fleet when its protections fit the work and your team can maintain them.
Frequently Asked Questions
What security features should I require in a business laptop?
Start with the work and information the laptop will handle. Common requirements include Secure Boot, hardware-backed credential protection, encryption support, reliable firmware and operating-system updates, and compatibility with centralized device management. Specify how each feature must work so your team can verify it.
How long should a device receive security updates?
There is no single support period that fits every organization. Confirm the vendor’s documented commitment, then align your replacement plan with the device’s expected use, the sensitivity of its work, and any contract or policy requirements. Schedule a review before support ends so migration does not become a last-minute scramble.
Is a more expensive device always more secure?
No. Price alone does not prove update support, management compatibility, or supply-chain transparency. Compare documented capabilities and the cost of operating the device securely; an affordable model with clear support may suit a role better than a premium model with unclear commitments.
Should we standardize on one hardware model?
A small, tested set of models can simplify configuration, support, spare parts, and incident response. Some roles need different hardware, such as rugged devices for field work or specialized machines for accessibility. Add a model when it solves a clear need and your team can support it.
What should happen when a device reaches end of life?
Remove it from management and identity systems, securely erase storage, and record whether it will be reused, recycled, or destroyed. Check that it no longer receives sensitive data before it leaves organizational control. If it will be reused, confirm it remains supported and manageable for its new role.
How should we handle bring-your-own-device purchases?
Set rules for enrollment, minimum security posture, access to company data, support, and lost-device reporting. Keep work and personal information separate where your tools allow it, and limit access when you cannot verify the protections you require. A personal device may suit routine email but not access to sensitive systems.
Conclusion
Before you request quotes, build a short scorecard that ties each device to its real job, required protections, support window, and management plan. That single step makes hardware choices easier to compare and helps you spot a bargain that would be costly to maintain.
Remember: the safest purchase is one your team can keep updated, managed, and useful through retirement. Make the requirements clear before the boxes arrive.
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.